PIM for Groups: Stop Hand-Assigning Admin Roles Like It’s 1998
PIM for Groups is how you stop onboarding admins one role at a time. Think back to the last time you set up a new administrator. What did that workflow look like?
If it went like this, you’re in good company. Open PIM, search for the user, select Add assignments and pick Exchange Administrator. Back out, search again, add Intune Administrator. Repeat for User Administrator, then put the kettle on because another starter arrives on Monday.
Direct assignment works, but it doesn’t scale, and it makes audits miserable. A better pattern is to assign roles to a group and use PIM to control who gets into that group, when, and for how long.
In this guide I build a role-assignable group called PIM-Tier2-Admins in my lab and make José Teixeira and Olavi King eligible members through PIM. We’ll cover licensing, the activation settings that matter, access reviews, Microsoft Graph PowerShell and the gotchas that catch people out.
Never miss a guide: subscribe here and check out my YouTube channel.
The short version (for anyone reading this between Teams calls):
- Create a role-assignable group in Entra ID > Groups > All groups > New group by setting “Microsoft Entra roles can be assigned to the group” to Yes. You can’t change it later.
- Assign the Microsoft Entra roles to the group as Active. The group holds the permissions; nobody is in it yet.
- Bring the group under PIM management and make admins eligible members, not permanent ones.
- Require MFA or a Conditional Access authentication context, a justification and, for role groups, approval.
- Licensing: Microsoft Entra ID P1 for role-assignable groups, and P2 or ID Governance for every eligible user, approver and reviewer.
In this guide
What is PIM for Groups?
This is the part of Microsoft Entra Privileged Identity Management that gives users just-in-time membership or ownership of a group. Until January 2023 it was called Privileged Access Groups, which is why that name still turns up in older blog posts.
A group on its own is just a list of people. What matters is what the group grants. Assign Microsoft Entra roles to a role-assignable group, make your admins eligible members, and activating that membership hands them every role in the group in one go.
So instead of mapping five roles to José, you map five roles to one group and one eligible membership to José. When his activation window ends, PIM removes him from the group and the roles leave with him.
Why direct role assignment becomes a trap
Onboarding is tedious. To fully onboard one administrator you might click through five or six separate role assignments, each with its own duration and settings.
Offboarding is risky. When someone moves teams or leaves, every assignment has to come off. Miss one and you’ve left standing privilege for the next auditor to find.
Visibility is poor. Ask who can manage Intune and you end up scrolling through individual accounts, hoping Dave from accounts didn’t get added as a “quick favour” two years ago.
Role-assignable groups vs PIM for Groups
These are two separate features, and they get mixed up constantly. A role-assignable group is created with the isAssignableToRole property set to true, which lets it hold Microsoft Entra roles. The PIM side is the just-in-time layer on top, and it works with any security or Microsoft 365 group that isn’t a dynamic membership group or synced from on-premises.
| Feature | Role-assignable group | PIM for group membership |
|---|---|---|
| What it does | Lets the group hold Microsoft Entra roles | Makes group membership or ownership eligible and time-bound |
| Supported groups | Security or Microsoft 365, assigned membership, cloud-only | Security or Microsoft 365, not dynamic, not synced |
| When it’s set | At creation only, can’t be changed | Any time, but a group can’t leave PIM once managed |
| Limit | 500 per tenant | More than 500 groups can be managed |
| Licence | Microsoft Entra ID P1 | Microsoft Entra ID P2 or ID Governance |
If the group holds Entra roles, it must be role-assignable. Even when a group only grants something sensitive, such as an Azure subscription or a key vault, creating it as role-assignable is worth considering. Only Global Administrators, Privileged Role Administrators and the group’s owners can manage it, and helpdesk-level roles can’t reset its members’ credentials.
Prerequisites and licensing
| Requirement | What you need |
|---|---|
| Role-assignable groups | Microsoft Entra ID P1 or P2 |
| PIM for group membership | Microsoft Entra ID P2 or Microsoft Entra ID Governance for each user with eligible or time-bound membership or ownership |
| Approvers and access reviewers | Also need Microsoft Entra ID P2 or ID Governance licences |
| Access reviews of PIM-managed groups (preview) | Microsoft Entra ID Governance or Microsoft Entra Suite |
| Create a role-assignable group | At least Privileged Role Administrator |
| Manage PIM for a role-assignable group | Privileged Role Administrator, Global Administrator or an active owner of the group |
| Scripting | Microsoft Graph PowerShell SDK (not the retired AzureAD module) |
Good to know: count approvers and reviewers when you work out licences. The eligible admins are obvious. The manager who approves two requests a year is the one who gets forgotten.
How to set up PIM for Groups in 7 steps
Here’s the lab: one role-assignable security group called PIM-Tier2-Admins, a few Tier 2 admin roles, and two admins, José Teixeira and Olavi King. Make a cup of tea first, because step 1 contains a one-way door.
Step 1: Create the role-assignable group
- Sign in to the Microsoft Entra admin centre as at least a Privileged Role Administrator.
- Go to Entra ID > Groups > All groups and select New group.
- Set Group type to Security (Microsoft 365 also works), name it PIM-Tier2-Admins and add a description.
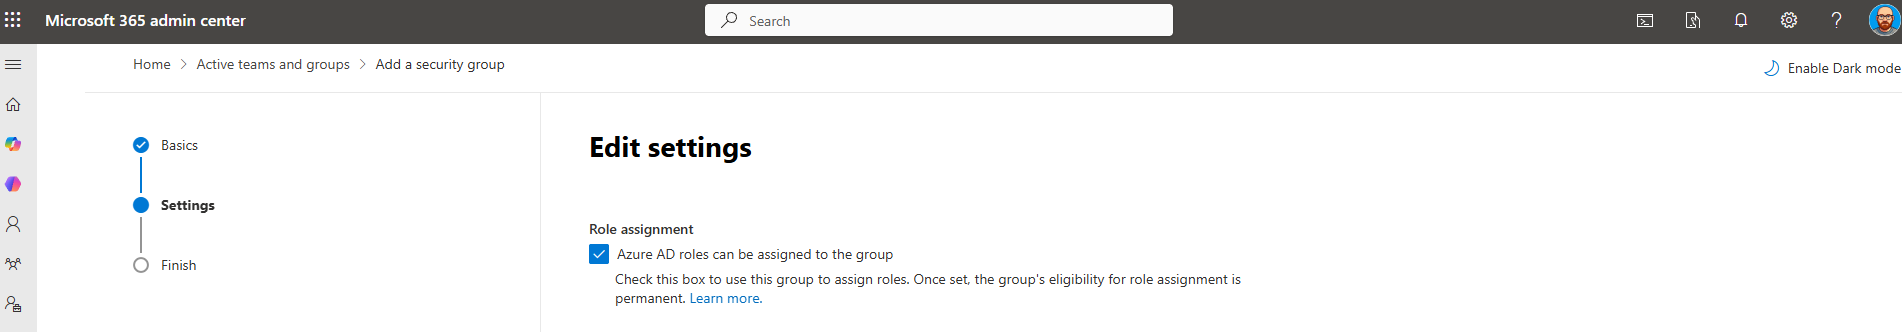
- Set “Microsoft Entra roles can be assigned to the group” to Yes. Membership type stays Assigned.
- Leave members empty. PIM will handle membership.
- Select Create, then Yes on the warning that this setting can’t be changed later.
Gotcha: the role-assignable setting only exists at creation. You can’t switch it on for an existing group, so forget it and the only fix is a new group. Check the toggle twice before you click Create at 4:55pm on a Friday.
You can also create the group from the Microsoft 365 admin centre under Teams & groups > Active teams and groups > Security groups > Add a security group, where the option sits on the Edit settings page. That’s the route I used in my lab, back when the label still said Azure AD.
Prefer PowerShell? This uses the Microsoft Graph PowerShell SDK. Setting isAssignableToRole needs the RoleManagement.ReadWrite.Directory permission as well as rights to create the group.
Connect-MgGraph -Scopes "Group.ReadWrite.All","RoleManagement.ReadWrite.Directory"

$group = New-MgGroup -DisplayName "PIM-Tier2-Admins" `
    -Description "Tier 2 admin roles, eligible membership via PIM" `
    -MailEnabled:$false -SecurityEnabled `
    -MailNickname "pimtier2admins" `
    -IsAssignableToRole:$true

$group | Select-Object DisplayName, Id, IsAssignableToRole
Step 2: Assign Entra roles to the group
- Go to Entra ID > Roles & admins and select the role name, for example Intune Administrator. Select the name, not the tick box.
- Select Add assignments and choose PIM-Tier2-Admins. Only role-assignable groups appear in the picker.
- With PIM licensed, set Assignment type to Active and tick Permanently assigned.
- Repeat for each role the tier needs, such as User Administrator.
The group now holds standing permissions, but nobody is in it. That’s intentional. The group describes what Tier 2 can do, and PIM decides who gets to be Tier 2 and for how long.
Tip: roles assigned to groups can also be scoped to an administrative unit. If Tier 2 should only manage one region or one school, pair this with administrative units in Entra ID rather than handing out tenant-wide User Administrator.
Step 3: Bring the group under PIM management
- Go to ID Governance > Privileged Identity Management > Groups.
- In the current experience, search for PIM-Tier2-Admins and select it.
- In the legacy experience, select Discover groups, tick the group, then select Manage groups and OK.
You can also enable PIM from the group itself, through its Privileged Identity Management page under Entra ID > Groups. In my tenant, the PIM Groups page now shows a banner saying the legacy experience stops working after 31 October 2026, so expect Discover groups to disappear.
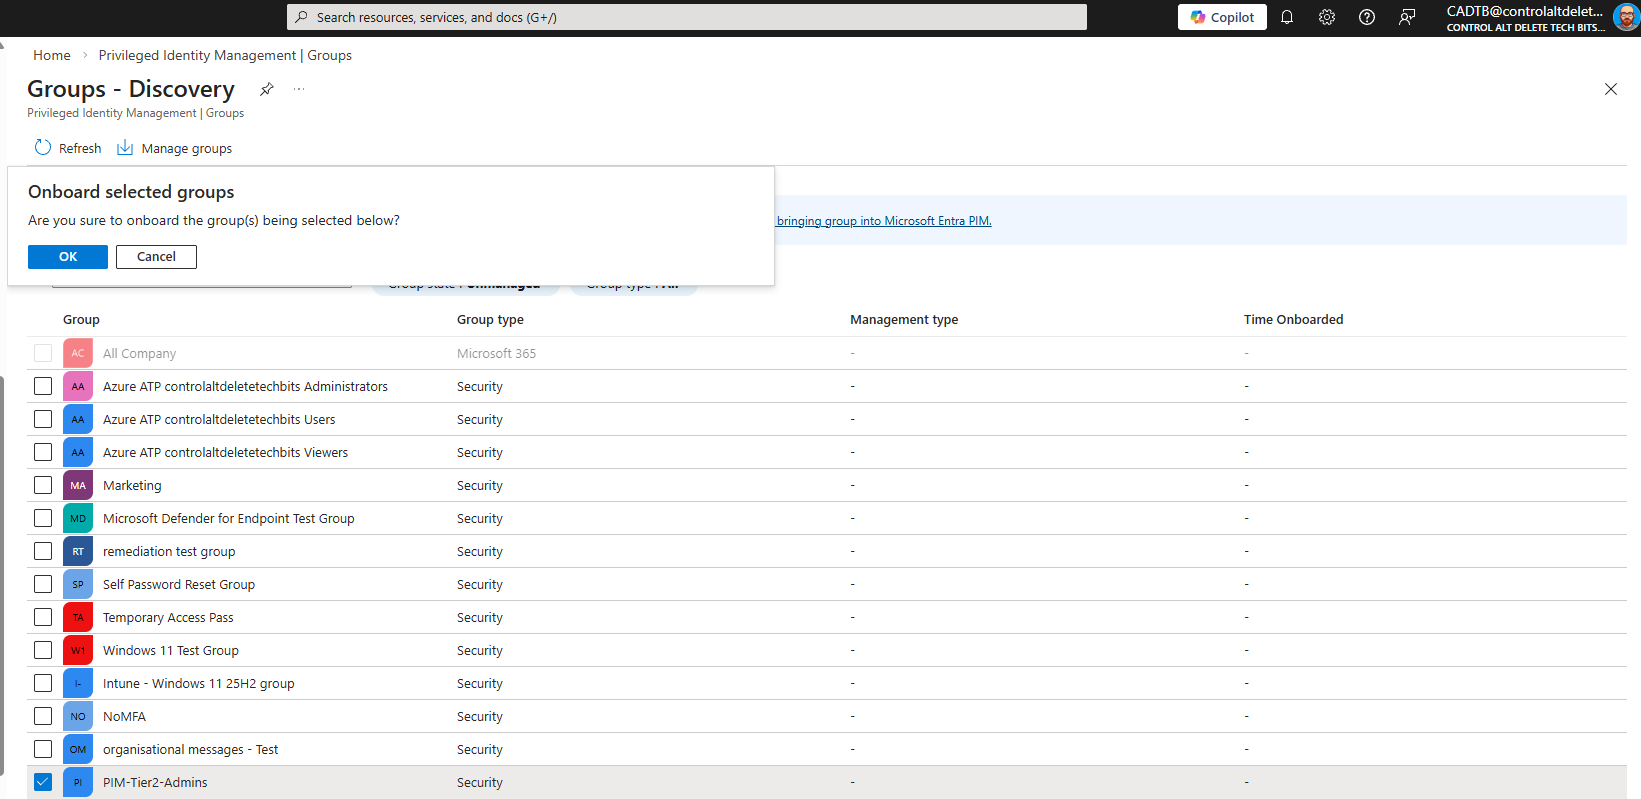
Gotcha: once a group is managed by PIM, you can’t take it out of management. That stops anyone quietly stripping the PIM settings, but it also means your test groups stay in the list forever.
Step 4: Configure the member and owner settings
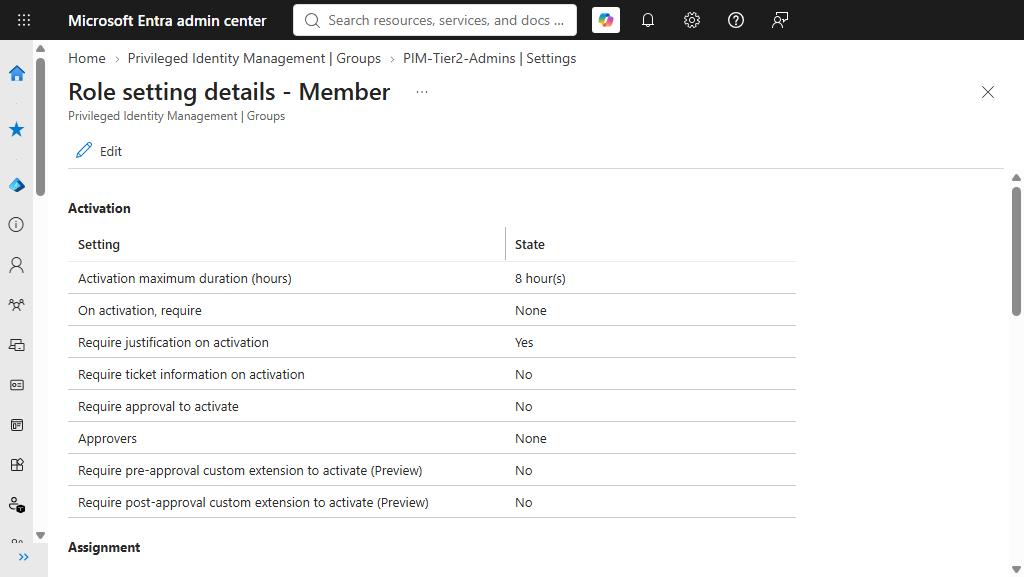
Each group has two separate policies, one for Member and one for Owner. Open the group in PIM, select Settings, choose Member, then Edit. Do the same for Owner, because an active owner can add people to the group, which is a back door if you leave it unguarded.
| Setting | What it does | My recommendation |
|---|---|---|
| Activation maximum duration | 1 to 24 hours | 4 to 8 hours for day-to-day admin work |
| On activation, require | None, multifactor authentication or a Conditional Access authentication context | Authentication context with a phishing-resistant authentication strength |
| Require justification on activation | User must type a reason | Yes |
| Require ticket information on activation | Free-text ticket number, not validated | Yes, if you run a service desk |
| Require approval to activate | Named approvers approve each request | Yes for role groups, with at least two approvers |
| Eligible assignment duration | Permanent, or expire after a set period | Expire, then renew through access reviews |
| Notifications | Emails to admins, assignees and approvers | Keep the critical alerts on |
Approval deserves a closer look. Without it, an admin who can reset an eligible user’s credentials could sign in as them and activate the membership. Role-assignable groups already limit credential resets on members to Privileged Authentication Administrators and above, but approval closes the gap properly.
If you use an authentication context, create and enable the Conditional Access policy first and scope it to all users or the eligible users. Don’t scope it to the group itself: at activation time the user isn’t a member yet, so the policy wouldn’t apply. Set sign-in frequency to Every time if you want a fresh sign-in for each activation.
My Microsoft Entra PIM guide covers authentication contexts for directly assigned Entra roles, and the same approach works here.
Step 5: Make admins eligible members
- In the group, select Assignments > Add assignments.
- Under Select role, choose Member.
- Select the users, in my case José Teixeira, then select Next.
- Set Assignment type to Eligible and choose the start and end dates.
- Select Assign.


José is now eligible, not a member. In my lab his eligibility runs for a year, the maximum this group’s settings allow. Pick Active instead and José becomes a permanent member with every role, all day, every day, which defeats the point.
To script it, use the Graph eligibility schedule request for groups. This makes Olavi King an eligible member for 180 days:
Connect-MgGraph -Scopes "PrivilegedEligibilitySchedule.ReadWrite.AzureADGroup","Group.Read.All","User.Read.All"

$group = Get-MgGroup -Filter "displayName eq 'PIM-Tier2-Admins'"
$user  = Get-MgUser -Filter "displayName eq 'Olavi King'"

$params = @{
    accessId      = "member"
    principalId   = $user.Id
    groupId       = $group.Id
    action        = "adminAssign"
    scheduleInfo  = @{
        startDateTime = (Get-Date).ToUniversalTime()
        expiration    = @{
            type        = "afterDateTime"
            endDateTime = (Get-Date).AddDays(180).ToUniversalTime()
        }
    }
    justification = "Tier 2 admin onboarding"
}

New-MgIdentityGovernancePrivilegedAccessGroupEligibilityScheduleRequest -BodyParameter $params
Step 6: Activate the group membership
- As the admin, sign in to the Microsoft Entra admin centre and go to ID Governance > Privileged Identity Management > My roles > Groups, or use aka.ms/pim.
- On Eligible assignments, select Activate next to PIM-Tier2-Admins.
- Complete the MFA or authentication context prompt if asked.
- Enter a reason, adjust the duration or start time if needed, then select Activate.
PIM adds the user to the group within seconds and removes them within seconds when the window ends. Some apps cache group membership, so if a portal still looks wrong, sign out and back in before blaming PIM.
Step 7: Review membership with access reviews
- Go to ID Governance > Access Reviews and select New access review.
- Select Review access to a resource type, choose Teams + Groups, then select PIM-Tier2-Admins.
- Choose reviewers, such as the group owners or a security lead, and a recurrence such as quarterly.
- Turn on Auto apply results to resource so denied users actually lose access.
A review of a PIM-managed group covers both eligible and active members, which is exactly what you want. The feature is still in preview and needs Microsoft Entra ID Governance or Microsoft Entra Suite licences.
Prove it worked
Before you tell the team the new model is live, check the plumbing from both ends.
- Entra ID > Groups > PIM-Tier2-Admins > Assigned roles lists every role the group holds. If Assigned roles is missing, the group isn’t role-assignable.
- Entra ID > Users > José Teixeira > Assigned roles shows the eligible access and whether it comes through a group.
- The group’s Resource audit in PIM records each activation, including the justification text.
- Activate as José, open the Intune admin centre, then let the activation expire and confirm the access disappears.
Or check both sides in PowerShell:
Connect-MgGraph -Scopes "RoleManagement.Read.Directory","PrivilegedEligibilitySchedule.Read.AzureADGroup","Group.Read.All"

$group = Get-MgGroup -Filter "displayName eq 'PIM-Tier2-Admins'"

# Roles the group holds
Get-MgRoleManagementDirectoryRoleAssignment -Filter "principalId eq '$($group.Id)'" -ExpandProperty RoleDefinition |
    Select-Object @{n='Role';e={$_.RoleDefinition.DisplayName}}, DirectoryScopeId

# Who is eligible for membership or ownership
Get-MgIdentityGovernancePrivilegedAccessGroupEligibilitySchedule -Filter "groupId eq '$($group.Id)'" |
    Select-Object PrincipalId, AccessId, Status
If the eligibility list is empty, check whether the assignment was created as Active by mistake, or whether someone added the user directly through the normal Groups page.
PIM for Groups gotchas
No nesting. A group can’t be an active member of a role-assignable group. A group can be an eligible member, and activation then applies only to the person who requested it.
No dynamic or synced groups. Role-assignable groups must use assigned membership and be cloud-only, and PIM can’t manage dynamic membership groups or groups synced from on-premises either.
Exchange, SharePoint and Purview roles. If eligible group membership grants a role such as Exchange Administrator, permissions can take a long time to work after activation. For those roles, use PIM for Entra roles directly, or keep users as active members and make the group eligible for the role.
The Groups page can override PIM. Admins and group owners can still add members through the normal Groups experience, and a permanent member added there skips PIM entirely. Your access review should catch it, but it’s worth a monthly look.
Groups that also grant app access. If the group assigns an app with provisioning, activation triggers provisioning that usually lands in 2 to 10 minutes. Busy periods get throttled and fall back to the 40-minute sync cycle.
Restricted management administrative units. PIM doesn’t support groups in restricted management administrative units, so keep your PIM groups out of them.
The 500 limit. A tenant can have up to 500 role-assignable groups. You can manage more than 500 groups in PIM, but only 500 of them can hold Entra roles.
Break glass accounts. Keep emergency access accounts out of PIM groups. They should hold Global Administrator as a permanent active assignment, as covered in my break glass account guide.
Last owner standing. Entra ID won’t remove the last active owner of a group, so if an eligible owner activates and the only other active owner then leaves, PIM can’t deactivate them. Keep a second active owner on every PIM group.
Should you use PIM for Groups?
For most tenants with more than a couple of admins, yes. Define what each tier can do once, attach it to a role-assignable group, and let PIM decide who steps into it, when, and for how long.
Imagine you hire Olavi King a week after José. Under the old model you repeat every role assignment. With the group model you open PIM-Tier2-Admins, add Olavi as an eligible member and you’re done: same controls, same audit trail, same access review.
It’s less suited to single-admin tenants, to Exchange or SharePoint roles that need fast activation, and to break glass accounts. For everything else, it beats clicking Add assignments until your mouse gives out like a Windows 98 ball mouse full of fluff.
PIM for Groups FAQs
Can I use a dynamic group with PIM for Groups?
No. Role-assignable groups must use assigned membership, and PIM can’t manage dynamic membership groups or groups synced from on-premises Active Directory.
Does a group have to be role-assignable to use PIM for Groups?
No. Any cloud security or Microsoft 365 group can be managed in PIM. It only needs to be role-assignable if you want to assign Microsoft Entra roles to it, though it’s recommended for any group that grants sensitive access.
Can I make an existing group role-assignable?
No. The isAssignableToRole property can only be set when the group is created and can’t be changed afterwards, so you need to create a new group.
What licence do I need for PIM for Groups?
Role-assignable groups need Microsoft Entra ID P1. Every user with an eligible or time-bound membership or ownership, plus approvers and access reviewers, needs Microsoft Entra ID P2 or Microsoft Entra ID Governance.
Can Microsoft 365 groups be role-assignable?
Yes. Both security groups and Microsoft 365 groups can be created as role-assignable, as long as they use assigned membership and are cloud-only.
What happens when a PIM for Groups activation expires?
PIM removes the user from the group within seconds and the roles assigned to the group go with it. Some apps cache group membership, so access in those apps may take a little longer to disappear.
Further reading
- Use Microsoft Entra groups to manage role assignments (Microsoft Learn)
- Create a role-assignable group in Microsoft Entra ID (Microsoft Learn)
- Privileged Identity Management (PIM) for Groups (Microsoft Learn)
- Configure PIM for Groups settings (Microsoft Learn)
- Create an access review of PIM for Groups (Microsoft Learn)
- Microsoft Entra PIM: set up just-in-time admin roles
- How to set up break glass accounts in Microsoft 365
- Why use administrative units in Microsoft Entra ID
Found this useful? Buy me a coffee, and if you handle subject access requests, have a look at Redact Ninja for redacting PDFs without sending files to a server.
Tags: Entra ID, Microsoft Entra
[…] You also might like this article […]
[…] PIM for Groups: stop hand-assigning admin roles […]