Intune App Inventory: Because ‘It’s Probably Installed’ Isn’t an Answer
Intune app inventory is the feature I wanted every time someone asked “which version of that is on the finance laptops?” and the only honest answer was a shrug.
Discovered apps has done the job for years, but it refreshes slowly and stops at a name, a version and a publisher. Intune app inventory goes further, collecting install locations, uninstall commands, sizes and whether an app is installed for the device or for one user.
Ideally you get those answers without a remote session where you ask someone to stop moving the mouse for a minute, please, Dave. App inventory gets you most of the way there.
This guide covers how to set up Intune app inventory with a Properties catalog policy, how it differs from Discovered apps, where the data comes from and how to read the results without jumping to conclusions. There are PowerShell checks along the way, all in proper code blocks this time.
Never miss a guide: subscribe here and check out my YouTube channel.
The short version (for anyone reading this while the licence auditor waits in reception)
- App inventory is switched on with a Properties catalog policy (Windows 10 and later) that includes the ApplicationProperties category. No policy, no data.
- It currently supports Windows 10/11 devices that are enrolled in Intune and Microsoft Entra joined.
- Results appear under Devices > All devices > device > All apps > App inventory. Allow up to 24 hours for the first collection.
- Discovered apps keeps running alongside it. App inventory is the intended long-term replacement, not an overnight one.
- Fleet-wide KQL queries for app inventory are listed as in development, so for now it is one device at a time.
- The Installed for column tells you the scope, not who ran the installer. Dave is not automatically guilty.
In this guide
I walk through the whole setup in my video, if you would rather watch someone else click the buttons:
What is Intune app inventory?
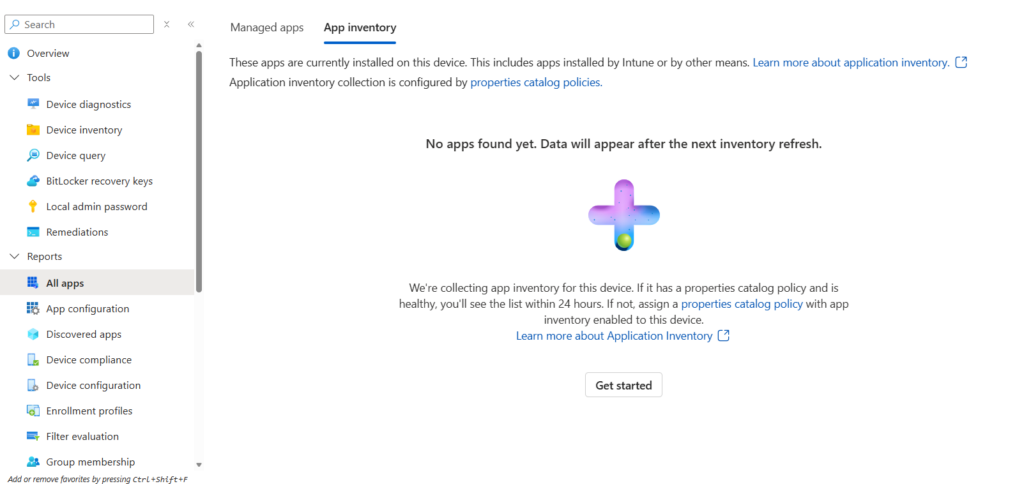
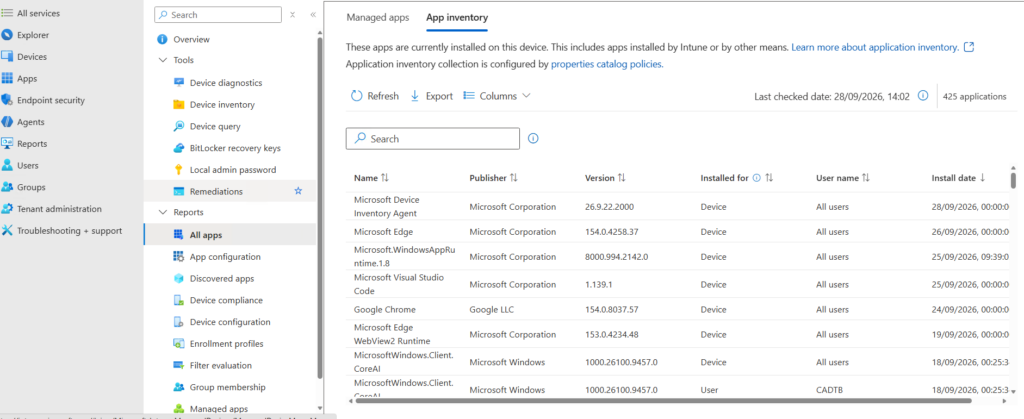
Intune app inventory is a policy-driven application inventory for Windows devices managed by Intune. The device inventory agent on each device collects app data and uploads it to Intune, where it appears on the device’s All apps page under the App inventory tab.
The useful distinction is between what you told Intune to deploy and what Windows says is installed. An app assignment describes intent, while an inventory record describes what the endpoint reports, whether the app arrived through Intune, a golden image or someone with local admin rights and a free afternoon.
Because the data comes from the device, names and versions can differ from the labels in your managed app configuration. When troubleshooting, I establish what is installed first, then work out how it got there and whether it matches the intended deployment.
Intune app inventory vs Discovered apps
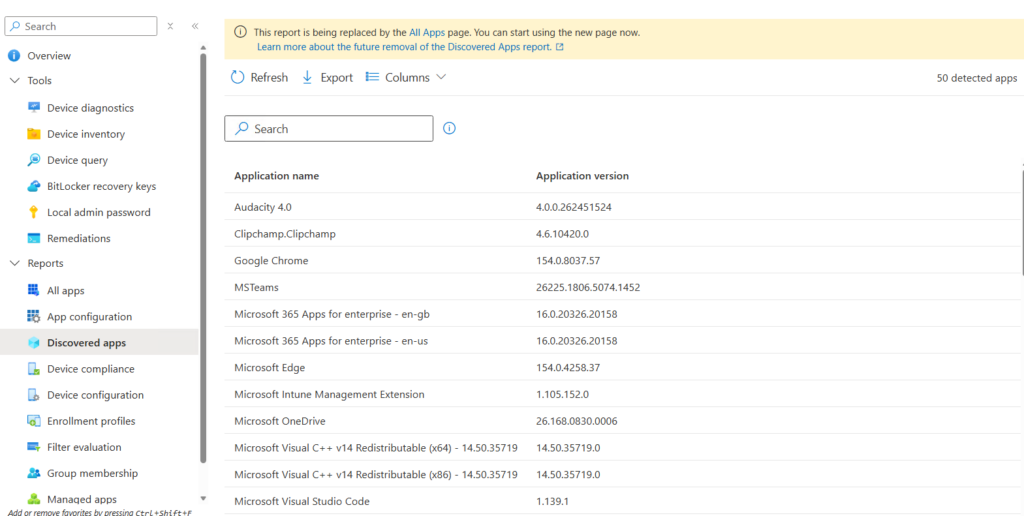
Discovered apps is still there and still useful. It collects automatically, covers more platforms and gives you a tenant-wide list under Apps > Monitor > Discovered apps.
Intune app inventory is the intended long-term replacement, but for now both run in parallel and enabling one does not switch the other off. Here is how they compare.
| Question | Discovered apps | App inventory |
|---|---|---|
| Needs a policy? | No, it collects automatically | Yes, a Properties catalog policy |
| Refresh cycle | Seven days per device (24 hours for Win32 data collected by the Intune Management Extension) | Multiple times per day on active devices |
| Data collected | Name, platform, version, publisher and device count | Those plus install location, install date, size, architecture, uninstall and modify commands, platform-specific ID, languages and install scope |
| Platforms | Windows, iOS/iPadOS, macOS, Android and AOSP | Windows (macOS, iOS/iPadOS and Android planned) |
| Where to find it | Apps > Monitor > Discovered apps, or per device | Devices > All devices > device > All apps > App inventory |
| Per-user installs | Last logged-in user | Multi-user support |
The refresh detail matters. Saying all Discovered apps data takes seven days is wrong, because Win32 app data gathered by the Intune Management Extension refreshes every 24 hours, but “multiple times per day” still beats both.
Also, do not confuse either report with Managed apps. A deployment status report tells you whether your assignment worked, not what else is hiding on the disk. If you are still building those deployments, my guide to deploying Windows apps with Microsoft Intune covers every app type.
Where does the Intune app inventory data come from?
The device inventory agent reads Win32 apps from the Windows uninstall registry keys at machine and user level, including 32-bit apps on 64-bit Windows. Store apps come from the Windows package manager, again at system and user level.
HKLM\Software\Microsoft\Windows\CurrentVersion\Uninstall
HKLM\Software\WOW6432Node\Microsoft\Windows\CurrentVersion\Uninstall
HKU\{SID}\Software\Microsoft\Windows\CurrentVersion\Uninstall
This explains a lot. Inventory quality depends partly on what the installer wrote to the registry, so a blank install location does not automatically mean Intune failed. It may simply mean the vendor never filled it in.
It also means Intune app inventory is not a recursive search for every executable on the disk. A portable app copied into a Downloads folder has no uninstall entry, so it will not appear here.
Good to know: the first sync uploads the full list, then later syncs send only changes (new, updated or removed apps). Your network team will not notice, which is the best kind of change.
Prerequisites and permissions
| Requirement | Detail |
|---|---|
| Device platform | Windows 10 or Windows 11 |
| Join and enrolment | Enrolled in Intune and Microsoft Entra joined |
| Policy | A Properties catalog profile with ApplicationProperties selected |
| Role to create the policy | Policy and Profile Manager, or a custom role with Organization/Read, Managed Devices/Read and Device configurations/Create, Read, Assign |
| Role to view the data | Managed Devices/Read |
| Cloud | Supported in GCC High, not in Microsoft Azure operated by 21Vianet |
Notice what is missing. Intune app inventory does not list Endpoint Analytics, Advanced Analytics or Defender for Endpoint as requirements, so there is no need to switch them on just because Device query documentation sits nearby.
Gotcha: the Properties catalog itself supports Microsoft Entra hybrid joined and co-managed devices, but the app inventory page currently lists Microsoft Entra joined devices only. If your estate is mostly hybrid joined, test a few devices before promising anyone a report.
How to set up Intune app inventory in 7 steps
Step 1: Confirm the device is Microsoft Entra joined
Start on a test device, because Intune app inventory currently needs Microsoft Entra joined Windows. Open PowerShell and check the operating system and join state:
Get-CimInstance -ClassName Win32_OperatingSystem |
    Select-Object Caption, Version, BuildNumber |
    Format-List

dsregcmd /status |
    Select-String -Pattern '^\s*(AzureAdJoined|DomainJoined|DeviceId)\s*:'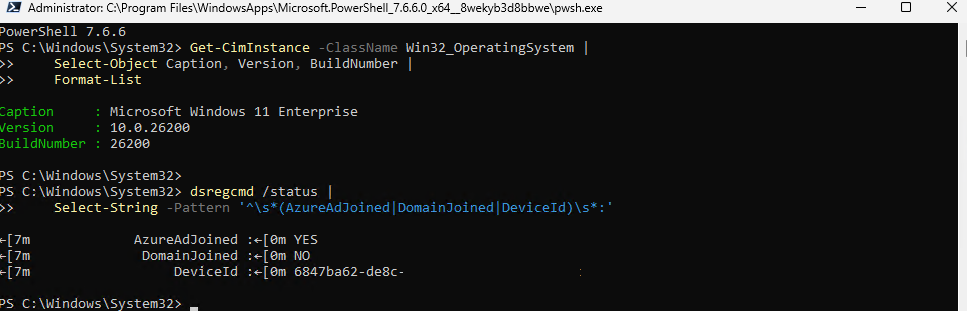
For a Microsoft Entra joined device, AzureAdJoined should be YES. DomainJoined helps you spot a hybrid joined device, and DeviceId is the value you compare with Intune in the next step.
Step 2: Check the Intune device record with PowerShell
Microsoft Graph PowerShell confirms which record Intune holds, its ownership and when it last checked in. Install the modules if you do not already have them:
Install-Module Microsoft.Graph.Authentication -Scope CurrentUser
Install-Module Microsoft.Graph.DeviceManagement -Scope CurrentUser
Then run this in one PowerShell session. It prompts for the device name and only reads data:
Import-Module Microsoft.Graph.Authentication
Import-Module Microsoft.Graph.DeviceManagement

Connect-MgGraph -Scopes 'DeviceManagementManagedDevices.Read.All' -ContextScope Process -NoWelcome

$DeviceName = (Read-Host 'Enter the device name as shown in Intune').Trim()

if ([string]::IsNullOrWhiteSpace($DeviceName)) {
    throw 'A device name is required.'
}

# Escape single quotes for the OData filter
$EscapedDeviceName = $DeviceName.Replace("'", "''")

$Devices = @(
    Get-MgDeviceManagementManagedDevice -Filter "deviceName eq '$EscapedDeviceName'" -All -ErrorAction Stop
)

if ($Devices.Count -eq 0) {
    throw "No Intune managed device record was found for $DeviceName."
}

$Devices |
    Select-Object DeviceName, Id, OperatingSystem, OSVersion,
        ManagedDeviceOwnerType, ManagementAgent, ComplianceState,
        LastSyncDateTime, AzureAdDeviceId |
    Format-List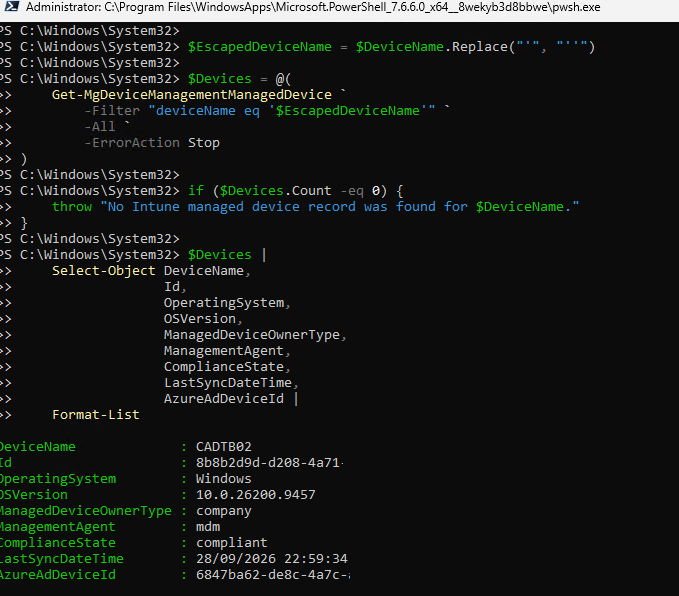
Compare AzureAdDeviceId with the DeviceId from dsregcmd, and check the last sync time. If several records share the name, investigate before picking one, and have a look at Intune device clean-up rules while you are there.
This script reads device metadata only. It does not retrieve the Intune app inventory report itself.
Step 3: Capture a local application baseline
Before Intune collects anything, record what the device says is installed. Run this in a 64-bit PowerShell session:
$Paths = @(
    'HKLM:\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\*',
    'HKLM:\SOFTWARE\WOW6432Node\Microsoft\Windows\CurrentVersion\Uninstall\*',
    'HKCU:\Software\Microsoft\Windows\CurrentVersion\Uninstall\*'
)

Get-ItemProperty -Path $Paths -ErrorAction SilentlyContinue |
    Where-Object { $_.DisplayName } |
    Select-Object DisplayName, DisplayVersion, Publisher, InstallLocation |
    Sort-Object DisplayName |
    Format-Table -AutoSize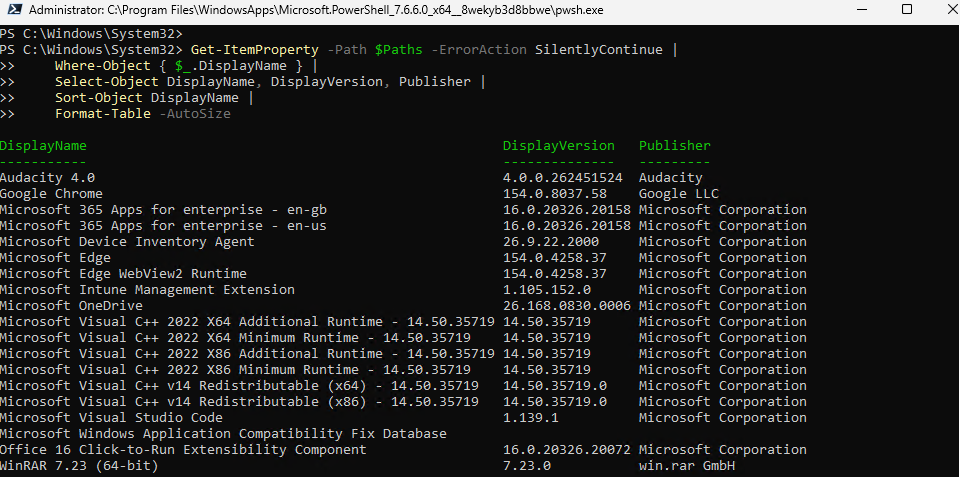
The HKCU line only covers the account running PowerShell, and Store apps are not included, so Intune app inventory will usually report more than this. That is expected.
I deliberately avoid Win32_Product. Querying it can trigger Windows Installer consistency checks and repairs, and reading an inventory should not turn into an unplanned maintenance window.
Step 4: Create a Properties catalog policy
- Sign in to the Microsoft Intune admin centre.
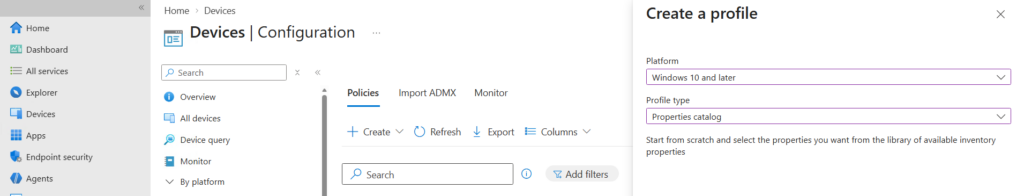
- Go to Devices > Manage devices > Configuration > Create > New policy.
- Set Platform to Windows 10 and later and Profile type to Properties catalog, then select Create.
- Give the policy a clear name, such as Windows App Inventory, and a description like “Collects Windows application inventory and installation metadata for troubleshooting.”
Step 5: Select Application Properties
In Configuration settings, select Add properties and tick the ApplicationProperties category. These required properties are added automatically:
- App Name
- App Version
- Publisher
- Architectures
- Install Scope
- Install Scope Platform User Id
- Install Scope User Id
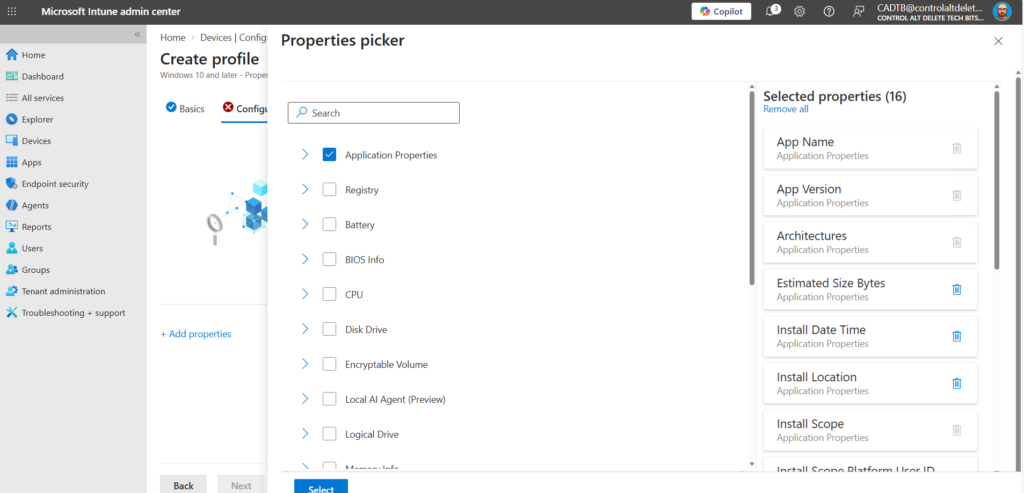
Then choose the optional properties. Not every app populates every field, because the data depends on what exists in the registry or the package manager.
| Property | Report column | Why collect it? |
|---|---|---|
| Install location | Install location | See where the app actually lives |
| Install date | Install date | Context for an investigation |
| Estimated size | Estimated size | Spot candidates for a storage conversation (reported in bytes) |
| Platform-specific app ID | Package Name | MSI product code or Store package full name |
| Platform Specific App ID Type | Platform Specific App ID Type | Which kind of identifier you are looking at |
| Uninstall command | Uninstall command | Check the registered removal command |
| Modify command | Modify command | The registered maintenance command |
| Languages | Languages | Reported app languages |
| Install Scope User Name | User Name | Makes user-scoped installs readable |
Tip: choose deliberately. User names and install paths deserve an access and data handling decision, not an enthusiastic click on every checkbox. Collecting an uninstall command does not run it either, so nobody’s apps vanish because you ticked a box.
Step 6: Assign to a pilot group and sync
Assign the policy to a small group of representative Windows devices, review the settings and select Create. Check the results on a handful of devices before you widen the assignment.
To hurry things along, open the device in Intune and select Sync > Yes. On Windows the sync action now runs a fuller sync across policies, apps and scripts, but a successful sync request is not proof the inventory has finished processing.
Collection starts at the next check-in and repeats several times a day on active devices. The first collection can take up to 24 hours, because the full sync runs once a day, so leave the device on and go and make a cup of tea. Possibly several.
Step 7: View the Intune app inventory results
Go to Devices > All devices, select the device, then All apps > App inventory. Search for an app from your baseline, then use Columns to show the optional properties you selected.
How to prove Intune app inventory is working
A big row count in Intune app inventory proves very little. Compare a handful of apps you know well against your baseline:
- Does the reported version match the local result?
- Is the install tied to the device or to a specific user?
- Do the populated fields match the app’s registry entry?
- Does Last checked show a recent date?
For a cross-check against Discovered apps, Graph PowerShell can pull the tenant-wide list. Swap in an app name you care about:
Connect-MgGraph -Scopes 'DeviceManagementManagedDevices.Read.All' -NoWelcome

Get-MgDeviceManagementDetectedApp -All |
    Where-Object { $_.DisplayName -like '*7-Zip*' } |
    Select-Object DisplayName, Version, Publisher, Platform, DeviceCount |
    Sort-Object DisplayName, Version |
    Format-Table -AutoSize
Expect timing differences between the two reports. Discovered apps may still show last week’s version while Intune app inventory already has the update, which is rather the point of the new feature.
How to read Intune app inventory results properly
Installed for does not mean installed by
The Installed for column tells you whether an app is installed for the device or for a specific user. A user name on a record identifies that scope, but it is not an audit trail proving that person ran the installer.
That makes Intune app inventory especially handy on shared devices, and a useful brake before you march over to Dave’s desk.
Repeated names are not automatically duplicates
Before deleting rows from an export, compare the identifier, version, architecture and user. Two rows with the same display name can be separate installs, such as 32-bit and 64-bit builds, or two users with their own copy.
Install date is not always the original install date
For MSI apps, the install date can change when the product is patched or repaired. Treat it as supporting evidence, not the sole basis for a “who installed this last Tuesday?” investigation.
Estimated size is an estimate
Use it to find candidates worth a look, not to promise everyone another 20 GB after an uninstall. If disk space is the real headache, Storage Sense in Intune is the gentler fix.
An uninstall command still needs testing
The registered uninstall command is a good starting point for packaging. Check the vendor’s documentation, silent switches, execution context and exit codes before pasting it into a Win32 app or a script in Intune Remediations.
Installed is not the same as used
A detected install does not prove anyone uses the app, that you own a licence for it, or that it is vulnerable. Correlate it with licensing, usage and security data, and use Intune Endpoint analytics for the device experience side.
What happens with multiple policies, or when you remove one?
If several Properties catalog policies target the same device, the device merges them. Where they conflict, “collect” wins over “don’t collect” for each property.
So editing one policy may not stop collection while another still asks for the same data. When chasing unexpected collection, review every policy that applies, not just the one with the obvious name.
Removing the policy is not an instant reset either. The agent keeps collecting app data for about three days, as a buffer for devices that are offline over a weekend, then collection stops and the app data is removed from the service.
That is separate from general Device Inventory data, where the last collected data stays visible for up to 28 days after you delete a Properties catalog policy.
Can you query Intune app inventory across all devices with KQL?
Not yet. Device query for multiple devices already works for hardware inventory, and Intune app inventory support for Windows is listed on the In development for Microsoft Intune page. As of 4 October 2026 it sits there, not in preview or general availability.
When it arrives, you should be able to use KQL to find versions, outdated software and unwanted apps across the estate without opening devices one by one. Device query for multiple devices is part of Advanced Analytics, so check your licensing as well as that page before you build a process around it.
Intune app inventory gotchas
No policy, no data. Unlike Discovered apps, Intune app inventory collects nothing until a Properties catalog policy with ApplicationProperties is assigned.
Portable apps. No uninstall entry means no inventory record, so that folder of portable tools on someone’s desktop stays invisible.
Patience. Allow up to 24 hours for the first collection. Refreshing the browser every 30 seconds does not speed it up, however satisfying it feels.
Logs. If nothing appears, check the device inventory agent logs on the device:
Get-ChildItem -Path 'C:\Program Files\Microsoft Device Inventory Agent\Logs' |
    Sort-Object LastWriteTime -Descending |
    Select-Object -First 5 Name, LastWriteTime, Length
You can also gather them remotely with the Collect diagnostics device action, which saves a trip to the third floor.
Should you turn on Intune app inventory?
Yes, turn on Intune app inventory for your Microsoft Entra joined Windows devices. It answers the question an app assignment cannot: what does the device report as installed, for whom, and where?
Start your Intune app inventory rollout with a pilot group, collect only the properties you need, and compare a few familiar apps against your PowerShell baseline. Once you trust the data, widen the assignment.
Just keep the caveats in mind. An inventory record is evidence to investigate, not proof that an app is healthy, licensed or used, and it is definitely not a signed confession from Dave.
Intune app inventory FAQs
What is Intune app inventory?
It is a Windows app inventory feature in Microsoft Intune that you enable with a Properties catalog policy. It collects richer data than Discovered apps, such as install location, uninstall command, size and install scope.
Where do I find app inventory in Intune?
Go to Devices > All devices, select a Windows device, then All apps > App inventory. It is separate from Managed apps and from the Discovered apps report.
Does Intune app inventory replace Discovered apps?
It is the intended long-term replacement, but both currently run in parallel. Enabling app inventory does not disable Discovered apps.
How long does Intune app inventory take to populate?
Allow up to 24 hours for the first collection, because the full sync runs once a day. After that, active devices report several times a day.
Does Intune app inventory work on hybrid joined devices?
The app inventory documentation currently lists Windows 10/11 devices that are enrolled in Intune and Microsoft Entra joined. The wider Properties catalog supports Microsoft Entra hybrid joined devices, so test before you rely on it.
Can I query app inventory across all devices with KQL?
Not yet. Device query for multiple devices support for Windows app inventory is listed as in development, so check the current In development page before planning around it.
Further reading
- App inventory for Windows devices in Microsoft Intune (Microsoft Learn)
- Use the Intune properties catalog to collect device properties (Microsoft Learn)
- Intune Discovered apps (Microsoft Learn)
- Device query for multiple devices (Microsoft Learn)
- How to deploy Windows apps with Microsoft Intune
- Intune Endpoint analytics explained
- Intune Remediations guide
If what you find turns into a packaging job, my video on deploying Windows apps with Intune is a good next stop:
Found this useful? Buy me a coffee, and if you handle subject access requests, have a look at Redact Ninja for redacting PDFs without sending files to a server.
You might also like my other projects, IntuneAccess and IdentityAtlas.
Tags: Intune
The installation scope column is the one I’d bring to licensing conversations. A title bought per device but showing up as per-user installs (or the reverse) is usually where the counts quietly stop matching what was purchased. And because App Inventory reports what it detects rather than what you assigned, it also shows the copies that arrived with an image or a manual install, which no purchase record will explain.
Until the multi-device KQL support lands, a practical way to use it is a spot check before a renewal: pick the few paid titles that matter, look at a sample of devices, and compare against the entitlement. It’s also worth checking whether any of those devices are marked retired or in stock in your asset register. If one is still reporting installs, it’s usually the register that’s out of date.
[…] How to Set Up Microsoft Intune App Inventory says: 29 September 2026 at 11:17 […]